Blog
Articles, tutorials, and field notes on identity, integration, API management, and application security — spanning nearly two decades of hands-on work.
Articles, tutorials, and field notes on identity, integration, API management, and application security — spanning nearly two decades of hands-on work.
REST web services are not nearly as formalized as their SOAP equivalent. A REST web service adheres to the principals laid out in Roy Fielding’s PhD Thesis. REST stands for Representational State Transition.
An XML Gateway is an externally-facing DMZ tier of a web services platform. Generally, this DMZ tier will be facing the Internet, but it may simply be between business units or facing a leased line connecting one entity to another. It can be implemented using a software solution (such as web…
I suppose I’m switching gears a bit here back towards something almost philosophical rather than my usual concrete technical info So be it. In the last six months, I’ve been at several clients sites that are using SOA appliances to build XML Gateway and ESB patterns. I answer quite a few client…
So, obviously, I haven’t posted anything here in a while🙂. Life has been busy. Starting several months ago, I left my job of four years and began independent consulting. Among other things, this means that the variety of topics discussed on thinkmiddleware.com should be more varied. I’m also going…
This is the first post on thinkmiddleware.com where we discuss DataPower. Guess what I’ve been doing with my career lately🙂.
On JBoss 4.x, a MySQL datasource looks something like:
On April 13th, 2011, Ryan Triplett and I spoke at IBM Impact in Las Vegas. The topic was “Secure Identity Propagation using WS-Trust, WS-Security, and SAML2“. The PowerPoint presentation can be found here. The original abstract:
I gave the following presentation at IBM Impact in April, 2011.
This article continues the discussion started in the Servlet Authentication article. Here we discuss Form-Based authentication; another common form of authentication when Servlet technology is used.
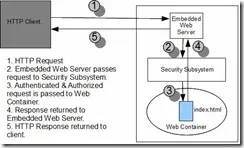
There are three required authentication mechanisms supported by a compliant Servlet Container: HTTP Basic Authentication, Form-based Authentication, and CLIENT_CERT authentication. There is a fourth authentication method, DIGEST, that isn’t used very often in my experience. This final…
If you were ever looking for a summary of each version of the J2EE Spec, it can take a few minutes to find it. So, here is a summary. The J2EE Specification is actually collection of numerous different Java-based technology specifications.
On June 24, 2010, I gave a presentation at JBoss World in Boston. This was my second time at JBoss World. The presentation covered Securing JBoss Services. It explored the use of JaasSecurityDomain MBeans to configure SSL in JBoss 4.3 (also relevent for newer versions of JBoss) for various…