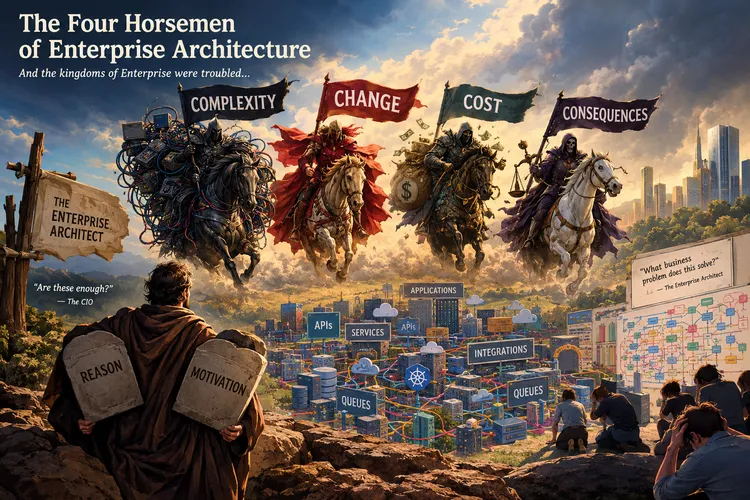
The Four Horsemen of Enterprise Architecture
And, it came to pass, in the latter days of Information Technology, that the Kingdoms of Enterprise were troubled.
RCBJ.NET
Two decades of field notes, tutorials, and hard-won debugging stories from building and securing large enterprise platforms — written by Robert Broeckelmann.
The RCBJ.NET blog is run by Iya Cyber Security Solutions, LLC (IyaSec), a boutique cybersecurity consulting firm specializing in application security, API security, identity, and API management. We have worked in the financial services, retail, and insurance industries, designing and implementing secure solutions for large enterprise platforms that service a wide variety of applications, as well as product development for technology companies.
We advocate a security-first architecture design approach to applications and systems. Our solutions follow a specification-based, vendor-agnostic philosophy to the greatest extent possible to avoid vendor and product lock-in. We specialize in multi-vendor solutions that involve heavy integration while maintaining security.
What you will find here is the working notebook behind that practice: protocol walkthroughs, configuration recipes, troubleshooting write-ups, and the occasional opinion piece — some of it written the same week the specification landed, some of it now a useful record of how these systems used to work.
The archive is deep. These are the subjects it returns to most often.
Field notes, tutorials, and deep dives on identity, integration, API management, and application security.
And, it came to pass, in the latter days of Information Technology, that the Kingdoms of Enterprise were troubled.
Based in the universe created by the The Tale of Thomas, Richard, and Karen — A Software Architecture Parable post.
Some organizations keep following the same legacy, bad practices even though they know better. They keep doing it right up until the unfortunate happens.
If you are looking for assistance or consulting services on the topics discussed here, we would be glad to hear from you.
Get in touch →