Blog
Articles, tutorials, and field notes on identity, integration, API management, and application security — spanning nearly two decades of hands-on work.
Articles, tutorials, and field notes on identity, integration, API management, and application security — spanning nearly two decades of hands-on work.
The OpenID Connect (OIDC) family of specs supports logout (from a single application) and global (or single) logout (from all applications that the user has logged into through the OpenID Provider, OP), but these features are optional or in draft status (as of Q2, 2017). So, these spec features may…
The following blog posts discuss SAML2 use cases that have been explored in this series:
The power of end-to-end user security context with APIs
Update(07/01/2019): This is by far my most popular post. I’ve continued to update this article based on feedback and things that I have noticed. I’m trying to keep it relevant.Please leave feedback in the comments section.
Extending OAuth2 and OpenID Connect as the enterprise standard for API security
The following blog posts make up my series on OpenID Connect. This is part of the SAML2 vs JWT series.
In part 1 and part 2 of Understanding OpenID Connect, core concepts and the first Authentication Flow (Authorization Code Grant Flow) were introduced. In part 3, we look at the remaining Authentication Flows (Implicit Flow and Hybrid Flow) and some other features of the OIDC specification.
This post continues our discussion of OpenID Connect (OIDC). We look at one of the three Authentication Flows defined by the OIDC spec — the Authorization Code Grant Flow.
This post builds upon what we learned about OAuth2 and JWT in previous posts. OpenID Connect will give us the final building block for the JWT-related use cases that this series will explore. The goal of this blog post is to provide a deep understanding of the OpenID Connect spec without having to…
This post was originally published as “Design Principles for Seamless User Authentication” on the Apigee Blog.
This post was originally published as “Keeping Your APIs Secure for Multiple User Types” on the Apigee Blog.
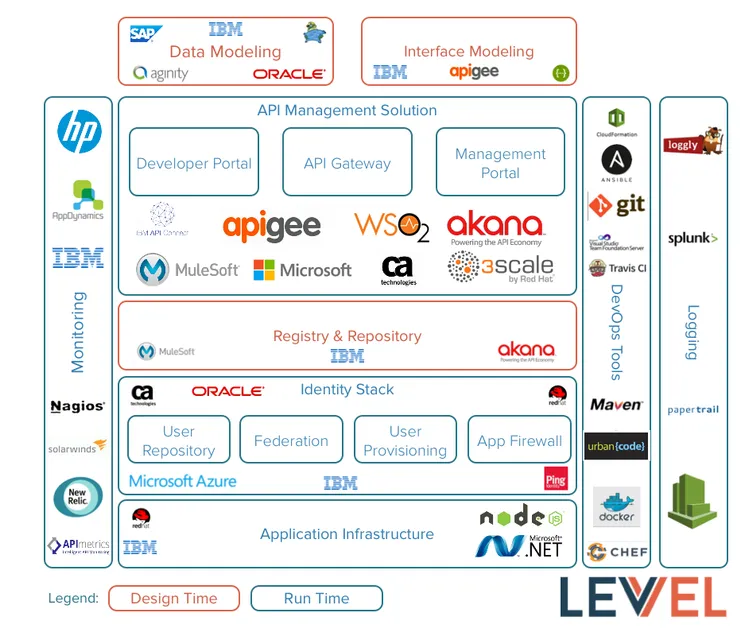
In the first three API Management posts I wrote, we discussed “What are APIs?(The Technical Perspective)”, “What is API Management?”, and “The Anatomy of an API Management Solution”. Continuing with this theme, we will explore the API Management Stack. So, what do I mean by API Management Stack?