Blog
Articles, tutorials, and field notes on identity, integration, API management, and application security — spanning nearly two decades of hands-on work.
Articles, tutorials, and field notes on identity, integration, API management, and application security — spanning nearly two decades of hands-on work.
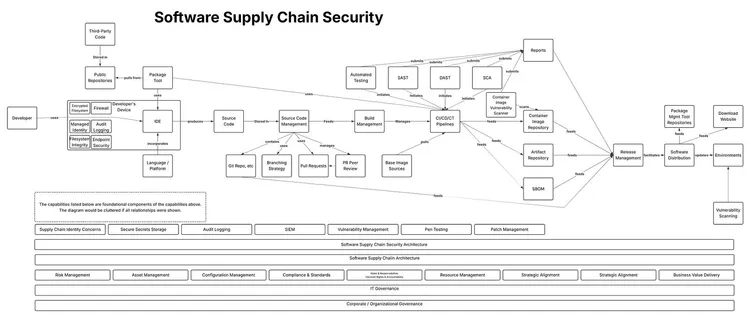
The DevOps movement of the last decade more-or-less led to the DevSecOps movement of this decade. This focus on automation to create efficient, end-to-end software publishing pipelines combined with incidents like the SolarWinds Hack in 2020 and the recent ‘S1ngularity’ attack on the NPM ecosystem…
For the small business owner, should the power going out mean you can’t make money? Should the computer system going down for 20 minutes mean a restaurant can’t take or cook orders any longer? Some basic level of preparation for anything other than ideal circumstances and commonsense needs to be…
For the small business owner, should the power going out mean you can’t make money? Should the computer system going down for 20 minutes mean a restaurant can’t take or cook orders any longer? Some basic level of preparation for anything other than ideal circumstances and commonsense needs to be…
Authentication is described in this post.
This post will introduce a generic set of database / datastore security requirements that be used as a starting point when developing a database security strategy.
First, let’s get the usual introductions out of the way. For an in-depth discussion of what Authorization is, check out this post. For a complete introduction to Authorization concepts see my Authorization Series. This post continues my long-running Authorization Series. In this post, we’re going…
Sometimes at client sites, I see a separation of APIs advertised on an API Gateway based upon consumer type. Sometimes, this is unavoidable, but there should be a core set of APIs and a general push to create APIs that are reusable. Reusability of APIs is a foundational building block of API…
For anyone who has been paying attention, this blog post has been a long-time coming for multiple reasons. First, this is my first blog post in a couple of years — I’ve been heads down on a couple of projects for awhile now. This is literally the first time I’ve “come up for air” since the last…
This blog post continues our discussion of Authorization in the API space. It will explore common authorization patterns with API Gateways and the backend API Providers. Generally, the API Gateway will apply a Coarse Grained Authorization (CGA) decision and the API Provider will implement Fine…
This blog post expands on delegation and related concepts introduced in my Kerberos Delegation blog post. It also brings together two blog series I’ve been working on over the years: SAML2 vs. JWT Series and Kerberos and Windows Security Series. Delegation is a critical building block of end-to-end…
In this next post in the Kerberos and Windows Security Series, we are going to explore a very useful, but abstract feature of the Kerberos Authentication Protocol: Delegation. In particular, we are going to focus on the Windows implementation of this feature. Delegation allows downstream actors to…
The use of HTTP POST vs HTTP GET for read-only (or query) operations in REST APIs recently came up in a conversation. For this particular shop, there had been a long-standing ban on the use of GET requests for use in homegrown applications. This had been the case since before REST APIs were in…